The update
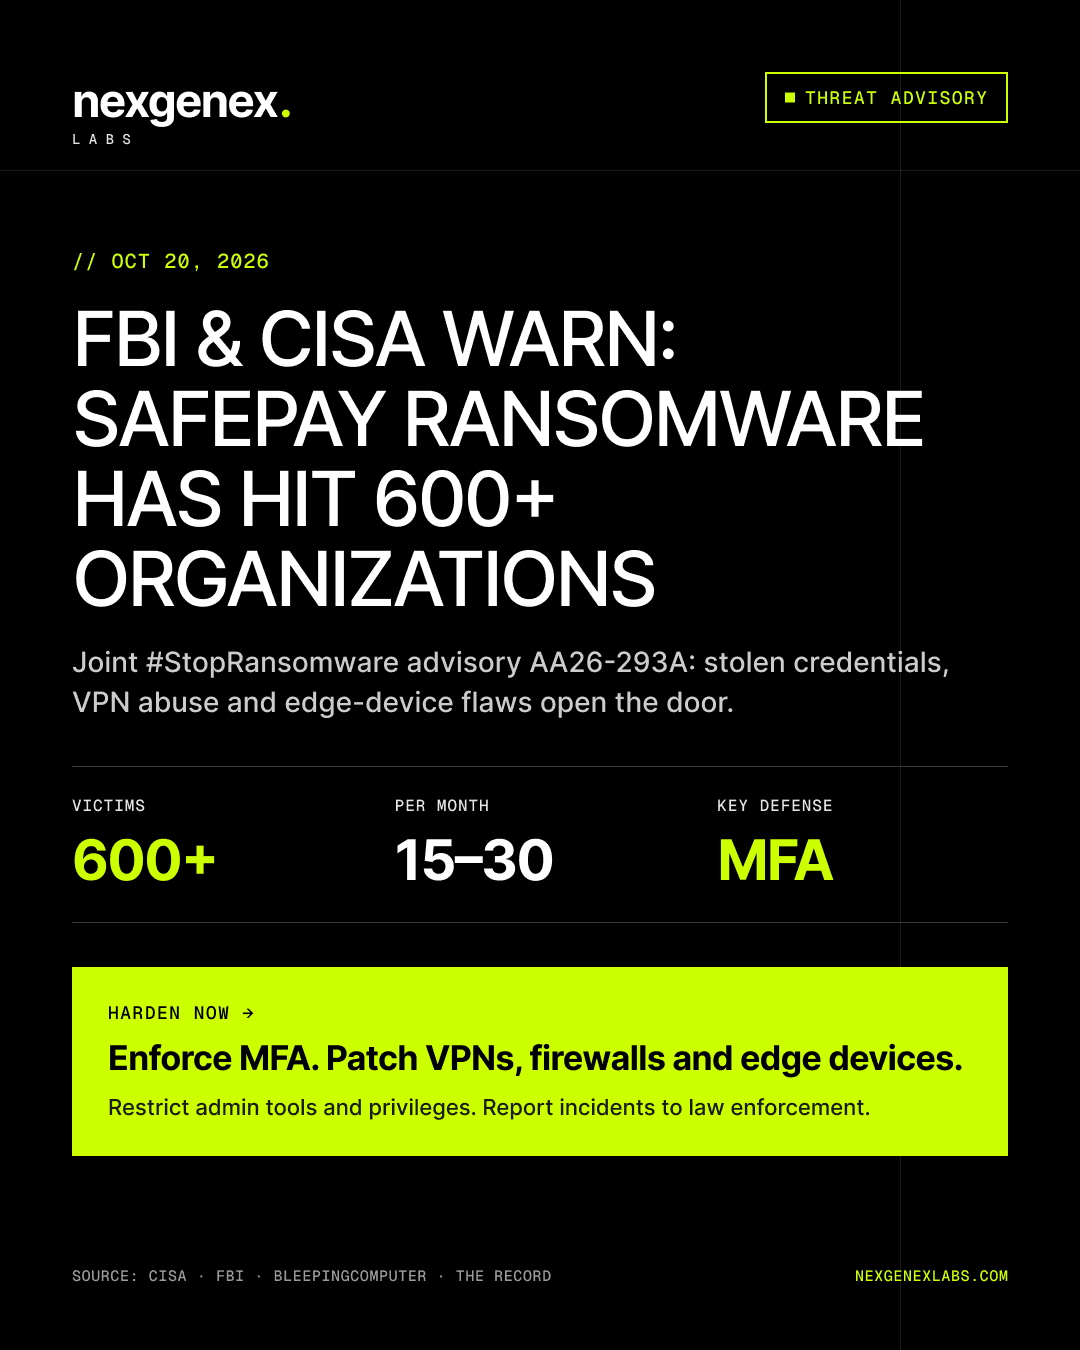
CISA, the FBI and international partners published #StopRansomware advisory AA26-293A on October 20, 2026, describing how the SafePay ransomware group operates.
Key facts
- At least 600 organizations affected since August 2024, across critical infrastructure sectors.
- Entry points: stolen or exposed credentials, brute force, VPN access, phishing and known edge-device flaws.
- SafePay steals data before encrypting it, deletes shadow copies and resets backup storage.
- Co-authored with the U.S. Secret Service, Germany's LKA Rheinland-Pfalz and the UK National Crime Agency.
What to do now
Enforce MFA, restrict admin tools, patch internet-facing devices first and keep an offline backup. Use our IT team checklist to work through the agencies' recommendations.
Sources
Have a project like this in mind?
Talk To Our Team →