The update
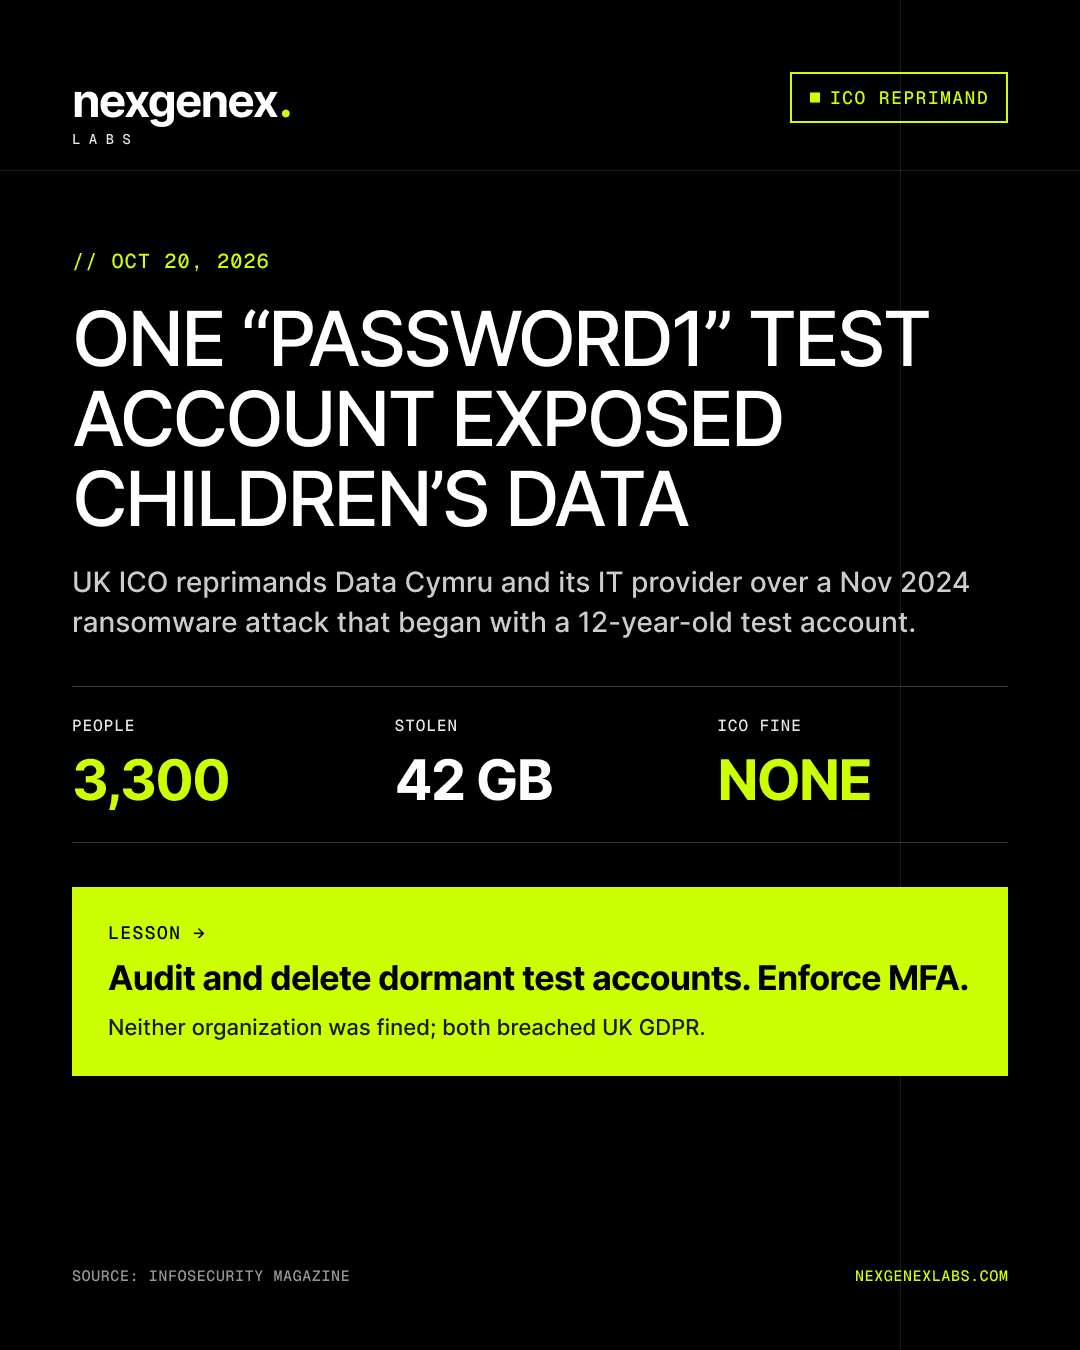
On October 20, 2026, the UK Information Commissioner's Office reprimanded Data Cymru and its IT provider, Ogi Networks, over a ransomware attack in November 2024.
Key facts
- Attackers entered through a test account called "Test 2", more than 12 years old, protected only by "Password1".
- 42GB stolen and 182.7GB encrypted; data on 3,300 people, most of them children, was affected.
- Both organizations breached UK GDPR. Neither was fined; both received reprimands.
What to do now
Audit dormant, test and vendor accounts, block common passwords and require MFA on remote and admin access. Our account-hygiene audit lists the steps.
Sources
Have a project like this in mind?
Talk To Our Team →