The update
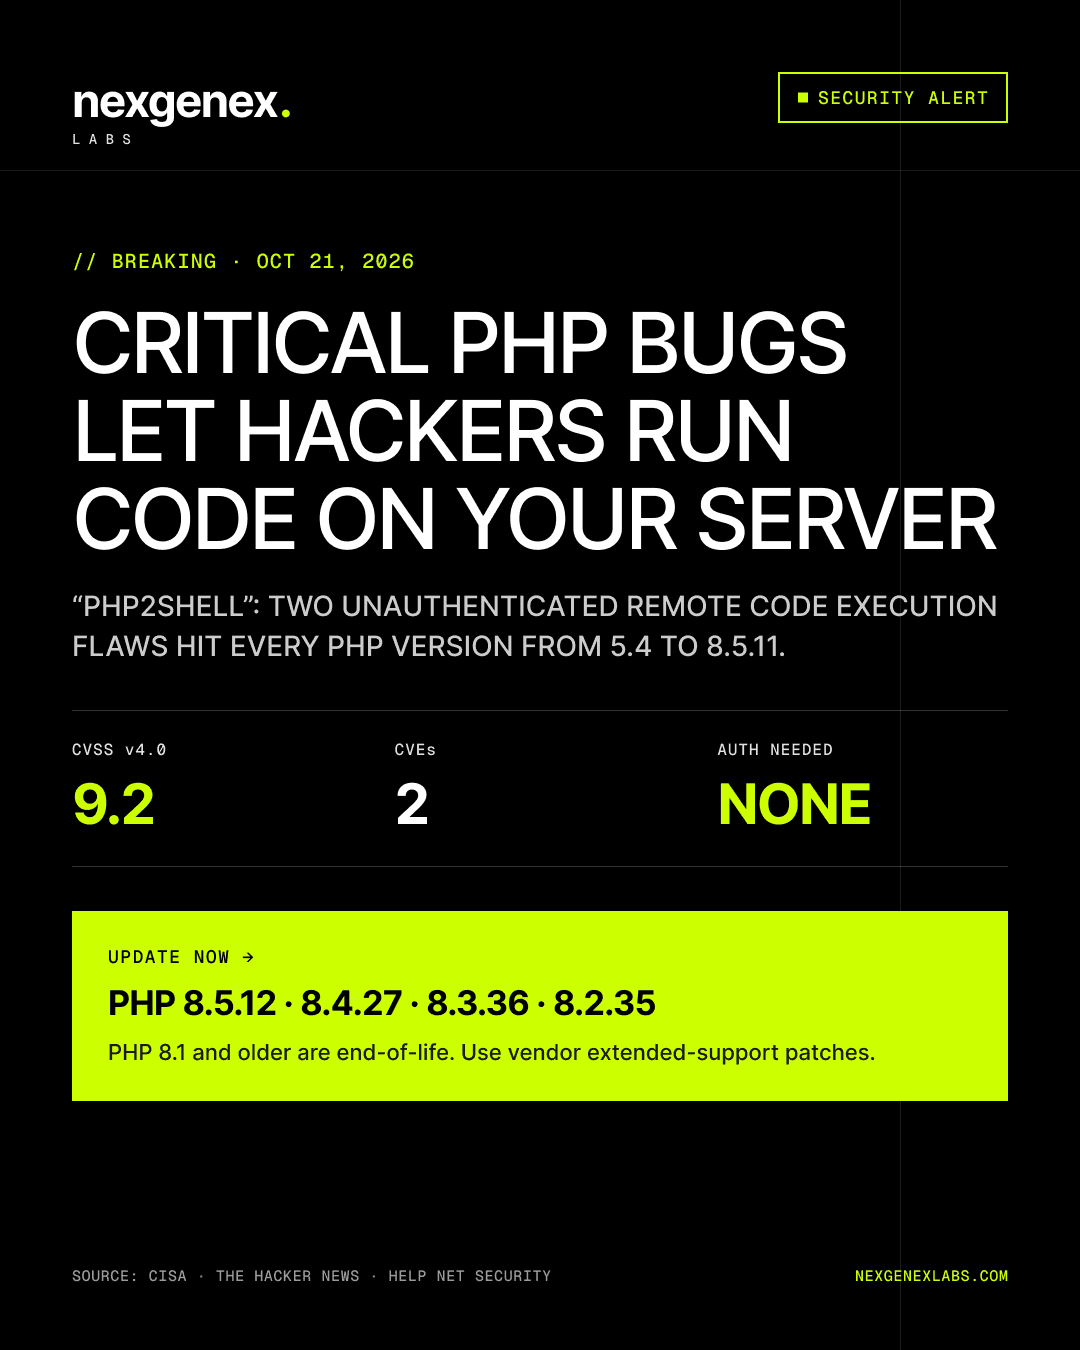
The PHP project released emergency security updates on October 21, 2026 for two critical flaws in the PHP runtime, nicknamed PHP2Shell. A leak on October 20 moved the release forward by a day.
Key facts
- CVE-2026-109618 (out-of-memory) and CVE-2026-109619 (session upload progress), both rated 9.2 on CVSS v4.0.
- No login needed: one crafted request can be enough on Apache
mod_php. - Affected: PHP 5.4 through 8.5.11. Fixed: 8.5.12, 8.4.27, 8.3.36, 8.2.35.
- Exploitation attempts have been reported; no confirmed compromise had been published at the time of writing.
What to do now
Update PHP, restart Apache, PHP-FPM and all workers, and check your Linux distribution's changelog for the CVE IDs. Read our full analysis and mitigation guide for stopgaps and signs of compromise.
Sources
Have a project like this in mind?
Talk To Our Team →